Security breach at Forever 21
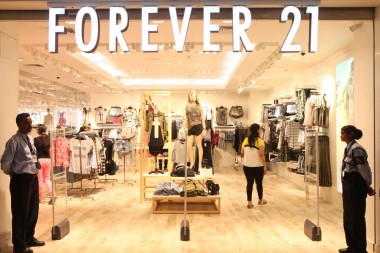
UPDATE: Forever 21's follow-up investigation of a data breach discovered in November has confirmed that malware was installed on some point-of-sale devices, and that some amount of personal payment card data was compromised. According to a statement from the retailer "the malware searched only for track data read from a payment card as it was being routed through the POS device. In most instances, the malware only found track data that did not have cardholder name — only card number, expiration date, and internal verification code – but occasionally the cardholder name was found." The retailer did not specify the number of stores or POS devices that were affected during the seven-month period in which the breach was ongoing.
November 2017: Forever 21, which operates 815 stores in 57 countries has said that there had been unauthorised access to data from payment cards at certain of its stores. The company has not named the stores. Investigations are being acrried out on transactions made between March and October this year. Only certain points of sale devices in certain stores were affected when the encryption on those devices was not operating.
IADS is launching an Innovation Lab on Cybersecurity and Risk Management in March
Innovation Lab on Cybersecurity
Related posts

Shein shares plunge 14% to record low after profit slides
Shein shares plunge 14% to record low after profit slides
Heading 1
Heading 2
Heading 3
Heading 4
Heading 5
Heading 6
Lorem ipsum dolor sit amet, consectetur adipiscing elit, sed do eiusmod tempor incididunt ut labore et dolore magna aliqua. Ut enim ad minim veniam, quis nostrud exercitation ullamco laboris nisi ut aliquip ex ea commodo consequat. Duis aute irure dolor in reprehenderit in voluptate velit esse cillum dolore eu fugiat nulla pariatur.
Block quote
Ordered list
- Item 1
- Item 2
- Item 3
Unordered list
- Item A
- Item B
- Item C
Bold text
Emphasis
Superscript
Subscript

M&S and Sephora enter partnership to bring new beauty destination to the high street
M&S and Sephora enter partnership to bring new beauty destination to the high street
Heading 1
Heading 2
Heading 3
Heading 4
Heading 5
Heading 6
Lorem ipsum dolor sit amet, consectetur adipiscing elit, sed do eiusmod tempor incididunt ut labore et dolore magna aliqua. Ut enim ad minim veniam, quis nostrud exercitation ullamco laboris nisi ut aliquip ex ea commodo consequat. Duis aute irure dolor in reprehenderit in voluptate velit esse cillum dolore eu fugiat nulla pariatur.
Block quote
Ordered list
- Item 1
- Item 2
- Item 3
Unordered list
- Item A
- Item B
- Item C
Bold text
Emphasis
Superscript
Subscript